This is kind of a long shot because I doubt very many people are reading the forums here anymore, but it can’t hurt to ask…
There’s an old knowledge-base post here that explains how to setup an enterprise AP to perform NAT for devices behind it. We are using this with the cnPilot e425h wallplate AP to act as a “home router” for small (low-income senior living) apartments.
My problem: the IP that the AP obtains on the wired network is what is used for both management access (cnMaestro), as well as where the customer traffic is NATed through.
Currently, if there’s no paying customer for the unit, the AP is “offline” to management, because it does not receive an IP, since our DHCP is integrated with RADIUS and only issues an IP to known/registered MAC addresses in our billing/CRM.
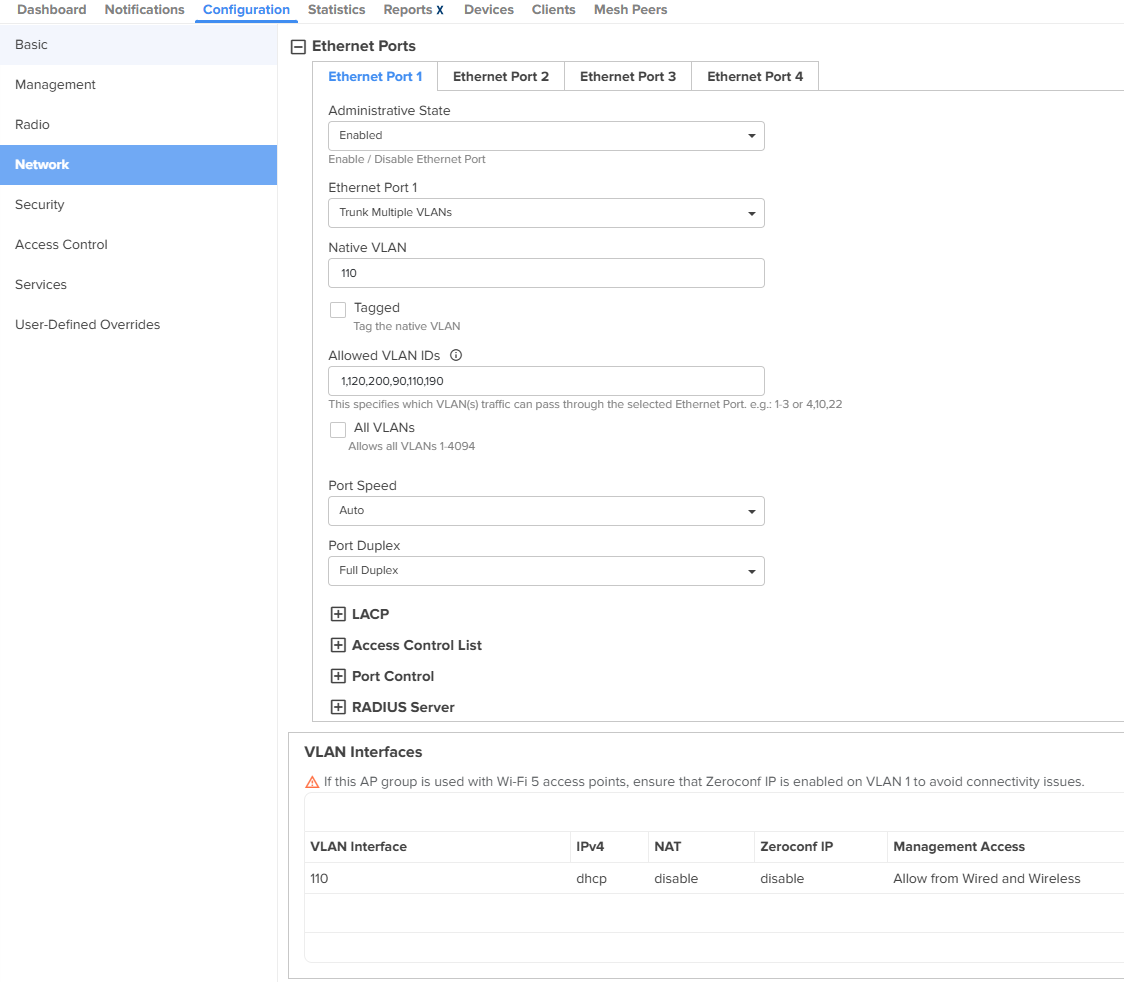
I know that I can have multiple VLAN interfaces on the AP. Is there any way to specify which one is used for management traffic and which is used to NAT the customer traffic? If I can keep the management on a distinct VLAN, and force the customer traffic to only be NATed through a different VLAN, this will allow me to handle customer access control via the DHCP server facing the customer VLAN, while still maintaining management access to the APs regardless of whether there’s a paying customer behind it.
All of this came up because I’m trying to migrate everything to onprem cnMaestro but half the APs at the site are “down” because they’re not associated to customers…